
AI Agents4 days ago
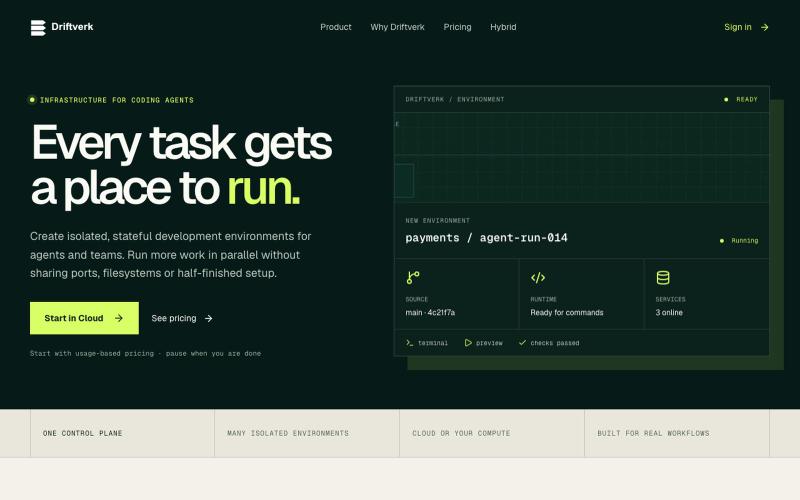
Driftverk | Infrastructure for coding agents
Create isolated, stateful development environments for coding agents and engineering teams.

@simskiiee · X
The full gallery
Tech stack
33 projects
Create isolated, stateful development environments for coding agents and engineering teams.
@simskiiee · X
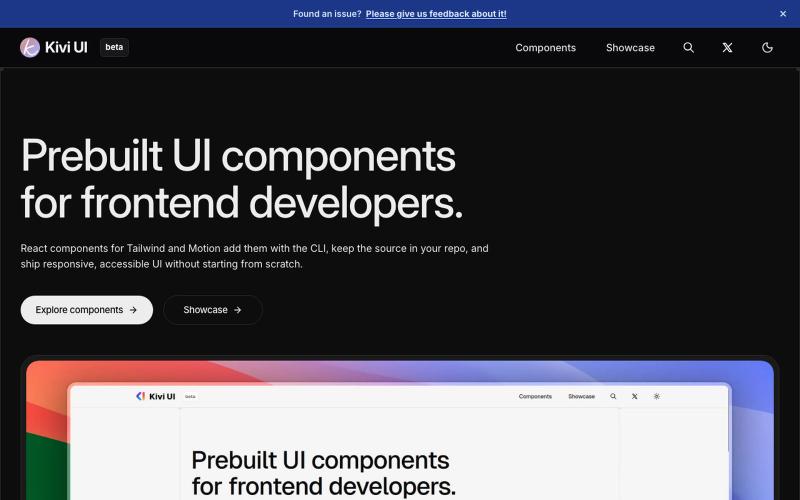
React component library with accessible, dark-mode-first components.

@JAY_VEGAD_ · X
Not a proper SaaS yet, just a small step in my journey. Feedback is always appreciated.

Map your company's AI attack surface to identify and defend against rogue AI vulnerabilities.

@yumahey · X
Everyone is vibe coding, almost no one is prepared for rogue AI attacking their company I created this platform to surface vulnerabilities that you can give to your AI to protect against
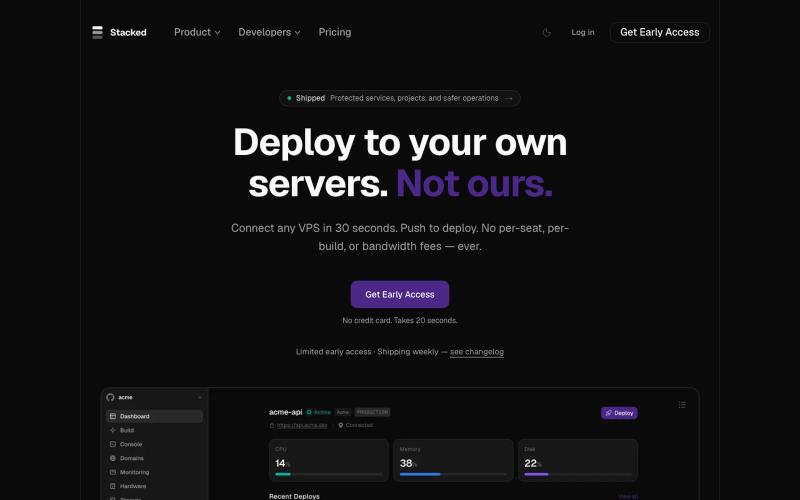
Self-hosted deployment platform offering Vercel-like developer experience on your VPS.

@ohdearkk · X
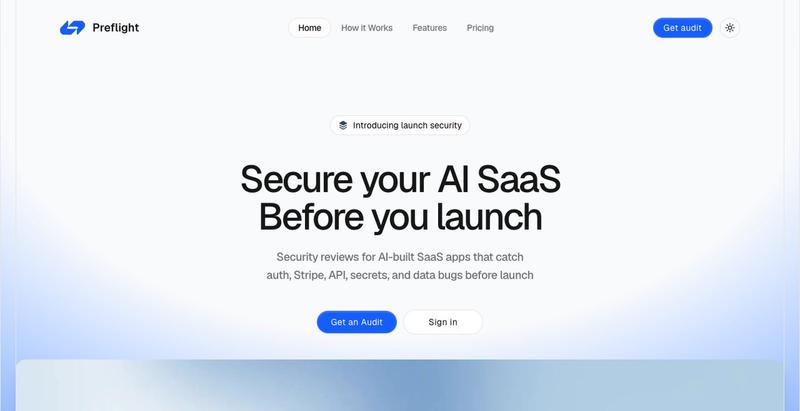
Automated security audits for GitHub repositories to catch secrets, auth issues, and deployment problems.

@emanueldev4 · X
Building Preflight a simple way to catch issues before your website goes live.
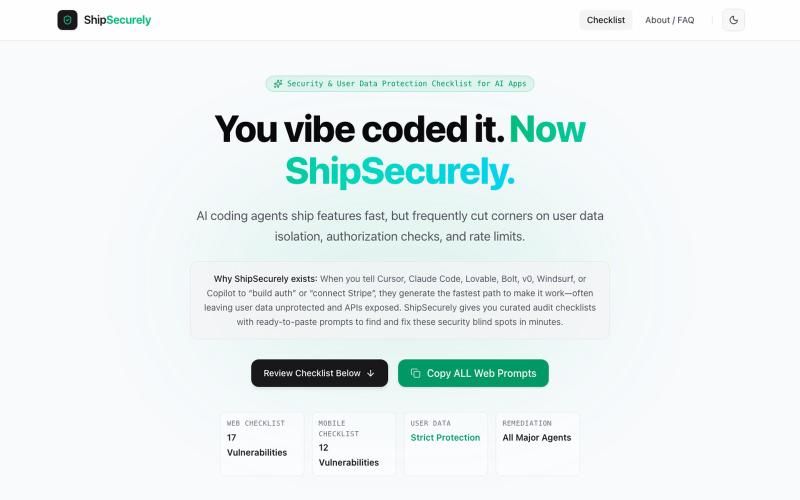
Free security checklist with copy-paste audit prompts for AI-built apps.

@zeeshan4015 · X
You vibe coded it. Now secure it. 🛡️ ShipSecurely — a free security checklist with 1-click audit prompts for Coding agents. Find and fix security vulnerabilities: Just copy paste the prompts to your coding agent and fix critical ones before launching

Scan your app for leaked API keys, open databases, and auth bypasses.

Nqspq
been building a security scanner for vibe-coded apps — it catches leaked API keys, open databases, logins you can bypass. tested it on a repo made for testing scanners. it caught everything — report below free if you want to check yours:
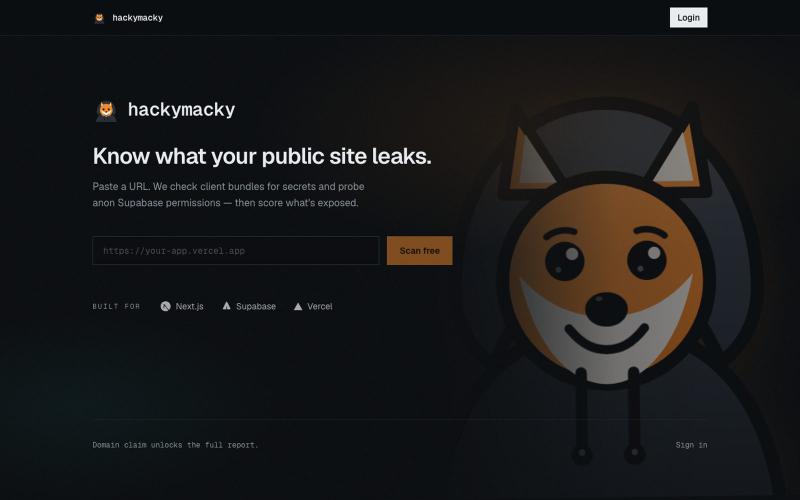
Paste a URL to scan Next.js and Supabase apps for security leaks and get a score.
civancza · HN
Security Scanning Tool
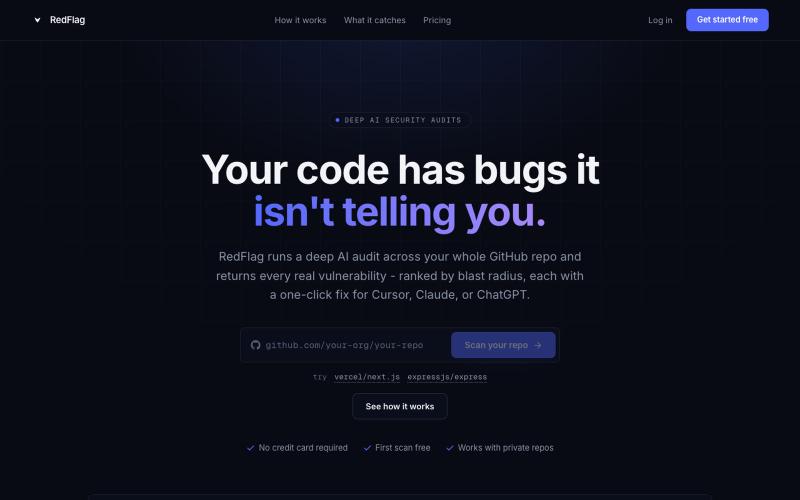
AI-powered security auditor that scans GitHub repos to find vulnerabilities and suggest fixes.
u/uwais_ish · Reddit
Three weeks to build an AI security scanner. The scanner was the easy part. Shipped RedFlag this month. Breakdown of where the time actually went, because it was nothing like I estimated. Stack: Next.js 16, Auth.js v5, MongoDB, Stripe, OpenAI. Deployed on Vercel. What I thought would be hard: getting an LLM to find real vulnerabilities. What was actually hard: getting it to stop finding fake ones. First working version flagged 200+ issues on a clean repo. Every one plausible, most of th