
Games & Play1 week ago
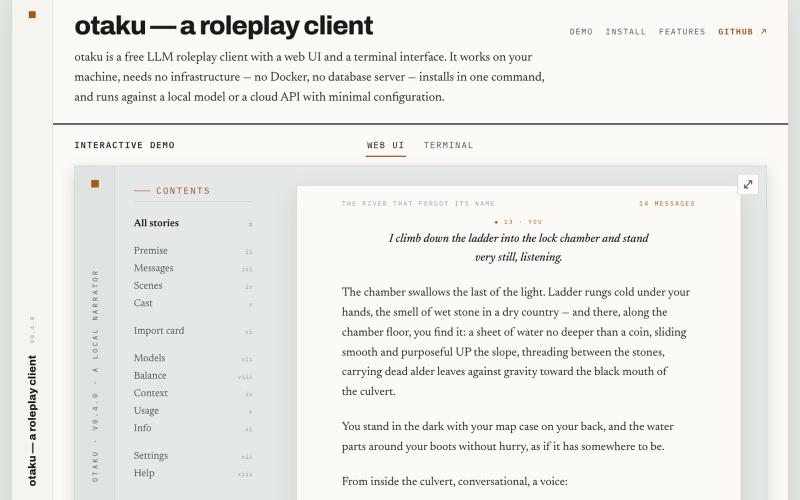
otaku — a roleplay client
Roleplay with AI using a web interface or terminal, powered by local or cloud LLM models.
Open source
enclavum5 · HN
Otaku.sh – AI Roleplay Client
The full gallery
Tech stack
60 projects
Roleplay with AI using a web interface or terminal, powered by local or cloud LLM models.
enclavum5 · HN
Otaku.sh – AI Roleplay Client
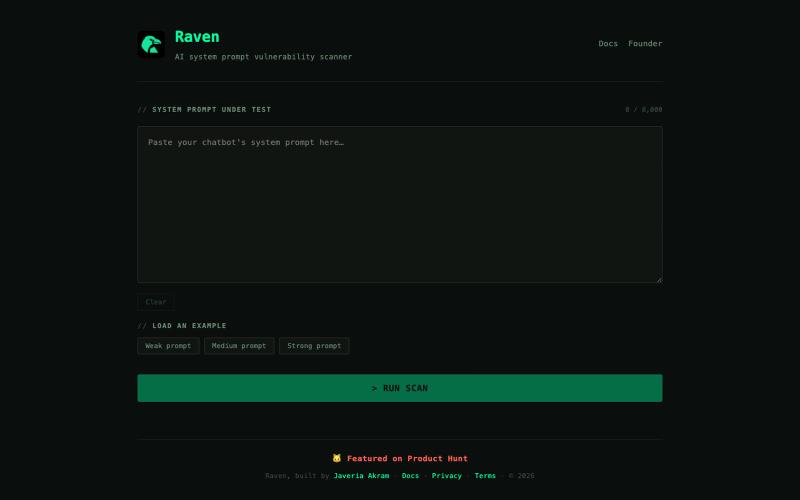
Test your AI system prompts for prompt injection, jailbreak, and information-leakage vulnerabilities.
javeria_akram1 · Product Hunt
Raven AI system prompt vulnerability scanner
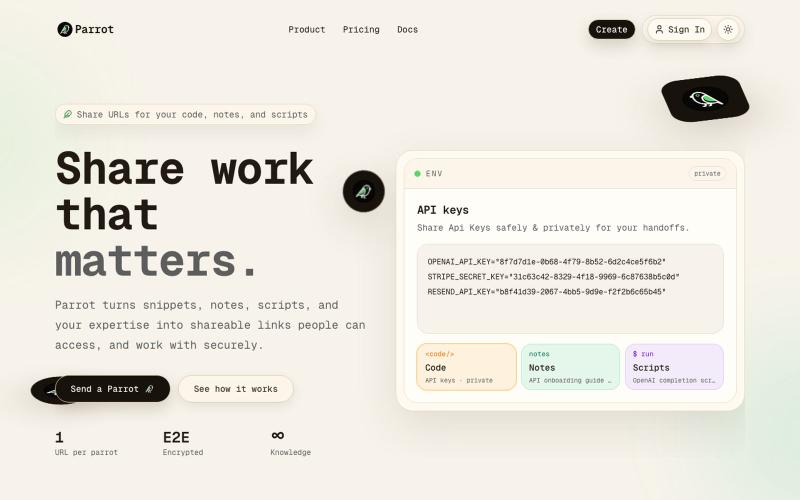
Share code, notes, scripts, and AI context via encrypted URLs.

@parrotwiki · X
one url. everything they need. code, notes, scripts, keys. end-to-end encrypted. 🦜
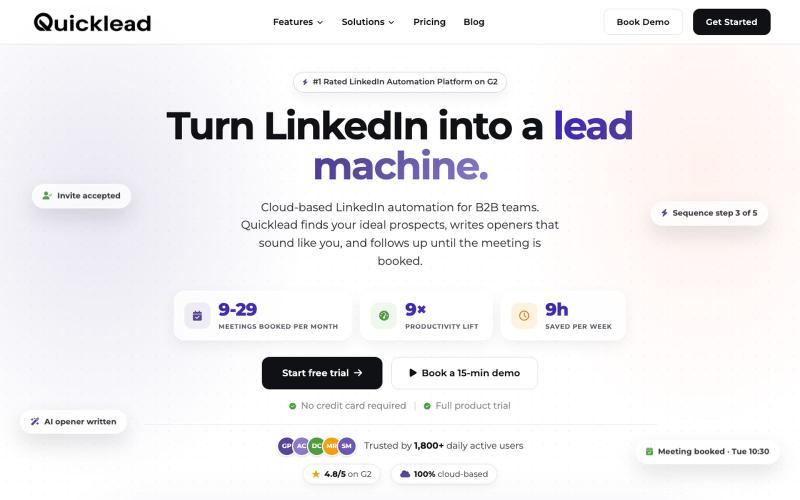
Quicklead is a cloud-based LinkedIn automation tool for B2B teams. AI ICP scoring, personalized sequences, free Open Profile InMails, smart inbox & CRM sync. Trusted by 1,800+ dail

@Parths049 · X

Scan vibecoded apps for security vulnerabilities including exposed keys, broken authentication, and missing row-level security.

@MrBallaz · X
Protect your vibe-coded app
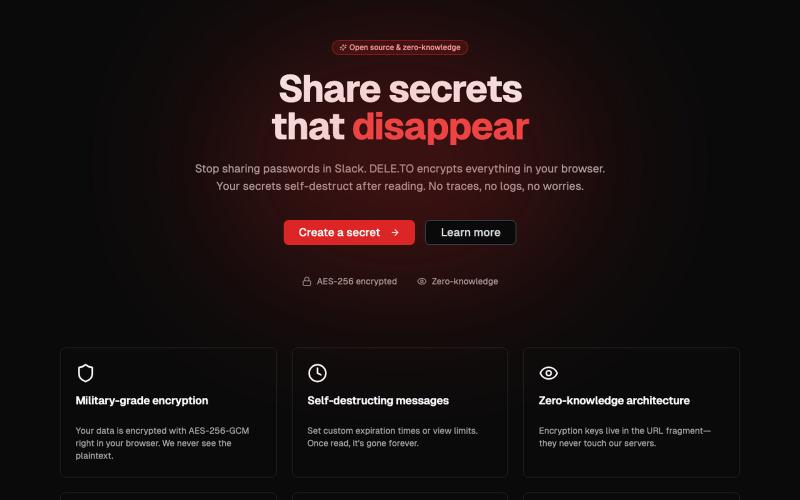
Secure credential sharing with client-side AES-256 encryption

@deleto_sec · X
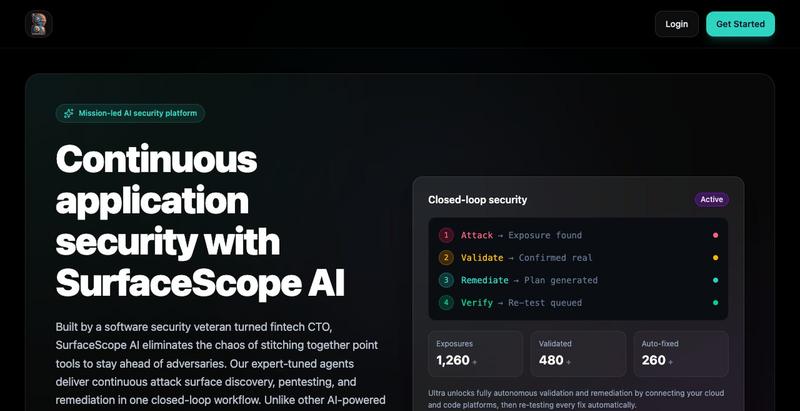
Analyze applications for security vulnerabilities with AI-powered scanning.

@DavidFilbey · X
I Built primarily using models from @AnthropicAI. However, I’m now completely unable to use any of the models to continue working on this app due to the extremely aggressive censorship and “guardrails” implemented. I have a premium subscription to Claude Code and Cursor. I’m curious to know if @cursor_ai or @AnthropicAI can provide a solution to allow me to continue using Anthropic models to develop legitimate security software products. Alternatively, I’d appreciate any recommendations you may have.

@RoundtableSpace a fun project! It will make you happy trust me! https://t.co/Xd0JH8yc3V

@Phoenix_I_am · X
a fun project! It will make you happy trust me!
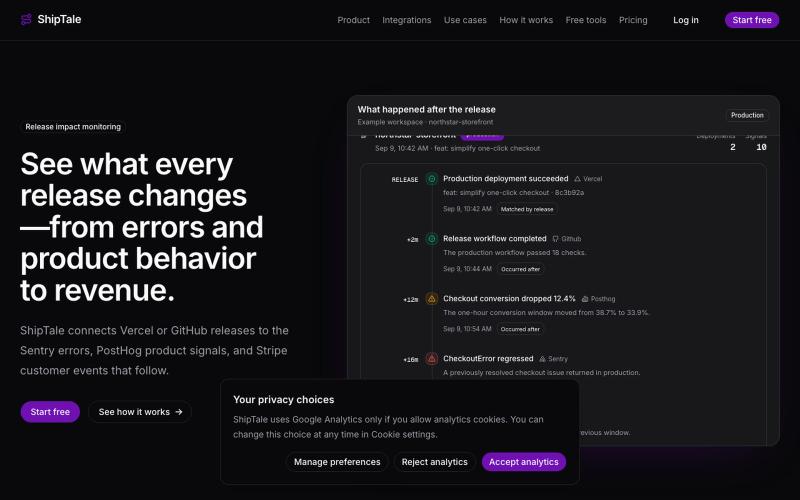
Connect Vercel or GitHub releases with Sentry errors, PostHog product measurements, and Stripe customer events in one production timeline.

@tronghiendev · X
Building ShipTale — helping devs see what broke after a deploy. Would love to connect.

Daily Hacker News stories delivered as an audio podcast in English and Turkish.
u/Noyis · Reddit
I built Hackercast — it turns Hacker News into a daily podcast you can listen I'm a developer who reads HN daily but kept running into the same problem: I'd open it on my commute, skim headlines, and never finish reading anything. So I built Hackercast. Every day it automatically: - Fetches the top 30 HN stories - Extracts the article content - Generates AI summaries (brief TL;DR + podcast-style deep dive) You get three depths per story: a 30-second brief, a 2-3 minute deep dive, o

Scans AI-built apps to find security issues like exposed databases, leaked API keys, and authentication flaws.

@Sentrint · X
Made Sentrint after seeing how many vibe-coded apps ship with RLS switched off. Point it at a GitHub repo and it finds open user tables, exposed keys and auth checks that only run in the browser. Free scan is the whole scan, no card.

@lightsilver323 https://t.co/mJ2scuQyV3

@radinodeapp · X