RepoMend
Scans code diffs for security secrets and code quality issues.
@RepoMend02 · X
Vibe-coded your MVP in a weekend? Cute. RepoMend reads every diff and hunts the secrets your AI forgot to redact. The auditor the AI forgot to build.
The full gallery
Tech stack
60 projects

Scans code diffs for security secrets and code quality issues.
@RepoMend02 · X
Vibe-coded your MVP in a weekend? Cute. RepoMend reads every diff and hunts the secrets your AI forgot to redact. The auditor the AI forgot to build.

Scan code and applications for vulnerabilities using AI-augmented security analysis.
u/swifi_ai · Reddit
After 10 years of keeping this idea alive, I finally launched my AI security platform to beta After more than 10 years of keeping this idea alive in one form or another, I finally pushed Swifi live to beta: https://swifi.ai Swifi is an AI-augmented application security platform. The goal: combine traditional security scanning with AI so teams can understand risk across code, vulnerabilities, and production context without stitching together a dozen disconnected tools. Why now? AI change

Secure GitHub pull requests with hardware authentication and OTP verification.
jallmann · HN
> want without a PR process that requires hardware authentication or proof of presence Just curious, what do you use for this? I built OTP Guard [1] a few years ago for exactly this problem, although I haven't seen any alternatives in the space. Does GitHub have something built-in now? The original framing was more "local malware compromising your GitHub account" ... it never occurred to me that the malware could be a LLM. I really should update the page. [1] https://otpguard.com

Chat with AI agents to scan web apps and APIs for security vulnerabilities.
@SableOffensive · X
Building Sable. An AaaS where specialized AI security agents perform penetration testing for web apps and APIs, helping teams find vulnerabilities before they reach production.

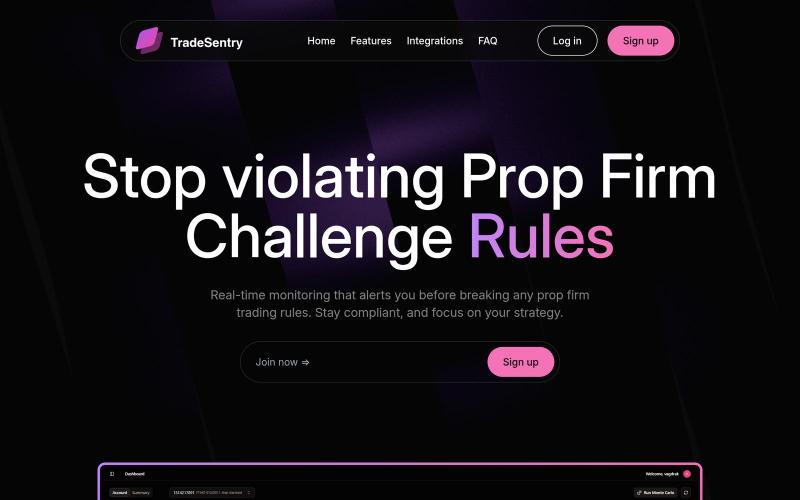
Real-time compliance monitoring tool for prop traders. Get instant alerts for rule violations, risk limit breaches, and time restrictions. Pass your prop firm challenge with confid
@vaggelisdrak · X

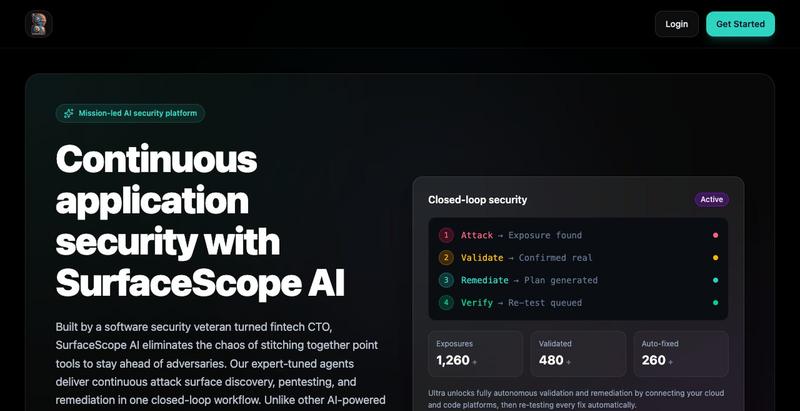
Analyze applications for security vulnerabilities with AI-powered scanning.
@DavidFilbey · X
I Built primarily using models from @AnthropicAI. However, I’m now completely unable to use any of the models to continue working on this app due to the extremely aggressive censorship and “guardrails” implemented. I have a premium subscription to Claude Code and Cursor. I’m curious to know if @cursor_ai or @AnthropicAI can provide a solution to allow me to continue using Anthropic models to develop legitimate security software products. Alternatively, I’d appreciate any recommendations you may have.

AI-powered platform unifying coding assistance, trading tools, and team collaboration features.
@ThrillStack · X

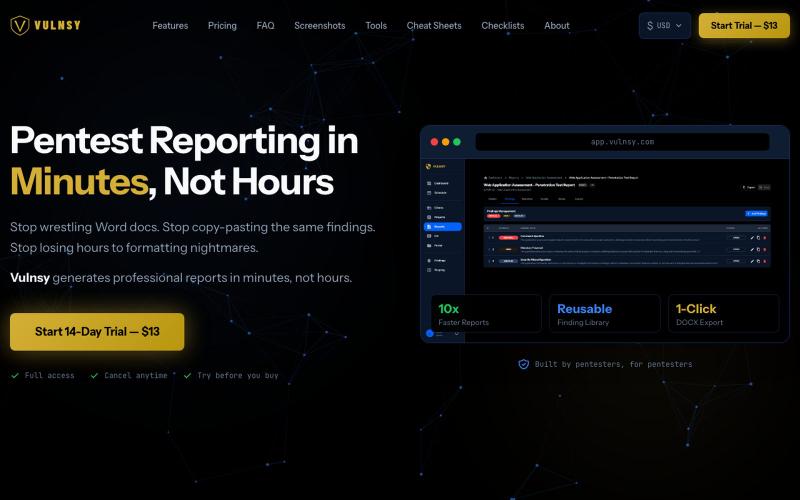
Platform for security teams to create and deliver penetration test reports faster with reusable findings and client portals.
@TurvSec · X

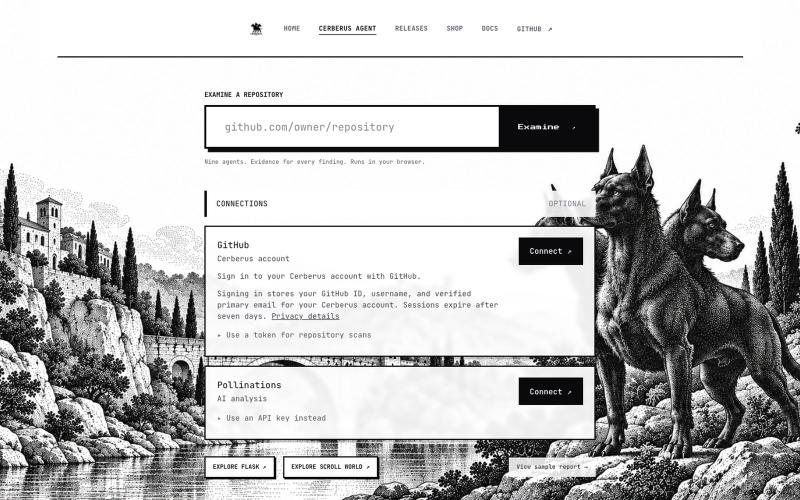
Run nine AI security agents to examine GitHub repositories, review findings, and export reports.
murderszn · HN
GPT 6 Astra gave me a reason to put the finishing touches on an old project, and I'm very content with where it landed. Back in June, I built Cerberus Agent as an AI "watchdog" for vibe-coded apps. The goal was to catch security issues before they turn into hacked apps, leaked credentials, or stolen data. Now its in production! Easier than I though it would be. It uses Pollinations as the AI backend to review GitHub repos, explain findings, and propose fixes. You can discuss the findings, inspec

Secure AI agent actions with code checks, permission gates, and approval workflows.
@RElharrak39428 · X

Sichtbarkeit, Backlinks, Rankings, Site-Audit und Security-Check an einem Ort. Ohne Anmeldung testen, mit Konto Projekte und tägliches Monitoring.
@cyberscaleio · X

Audit AI-built applications for security vulnerabilities and receive proof of findings.
u/mrtrly · Reddit
I asked ChatGPT 20 different ways who could fix a half-built app. It never named my company once. I do codebase rescue for founders in exactly that spot, so that one stung. There are already plenty of tools that measure this kind of AI visibility, a CDN even ships one free, so I built mine mostly to see my own number, and it confirmed the bad news: near zero. The measuring turned out to be the easy part. What none of the tools do, and what I actually care about, is the fix: getting the mode