

Utilities1 month ago
HuPow - Human Proof of Work
Use Proof-of-Work to verify senders are human and keep AI bots out of your inbox.
cmbza · HN
HuPow – Proof-of-Work to stop AI bots in your inbox
The full gallery
Tech stack
21 projects
Use Proof-of-Work to verify senders are human and keep AI bots out of your inbox.
cmbza · HN
HuPow – Proof-of-Work to stop AI bots in your inbox
Turn startup ideas into private proof links to validate customer fit.

@AshirShaikEng · X

A platform where founders share project logs, track progress, and discover what other builders are working on.

@yerassylnu · X
Github for founders

Scan your website for security vulnerabilities and compliance gaps against GDPR and CCPA standards.

@AICybershieldTe · X
Most sites are one scan away from a very bad day. Scanned ~100 this week — exposed .env files, missing security headers, cookies set before consent (a real GDPR fine). Security + privacy + accessibility, one 90s check: #vibecoding #buildinpublic
Structures verifiable evidence of AI usage in compliance processes.

@polsia · X
Vibe-coding an MVP takes a weekend. Auditing which bit was AI-written under EU Art. 50 — that's the part nobody ships.
Track and verify your deep work and focus time, completely private, solo or with friends.
u/penwonder · Reddit
Failed 3 times :) now satyashift gets around 50+ active users everyday :) http://satyashift.com how a simple web app + ext made focus better for online research and time management. through 6 months of constant feedback loop and reiteration , I can now finally say, satayshift is going to help you with your online work much better with the proof that you can see about your work. especially given the fact that most of us use different online platforms like AI platforms , e
Scan Supabase apps for security issues: leaked keys, missing RLS, and public buckets.

@urti_luca · X
Sentris finds the exposures in your Supabase app before someone else does.
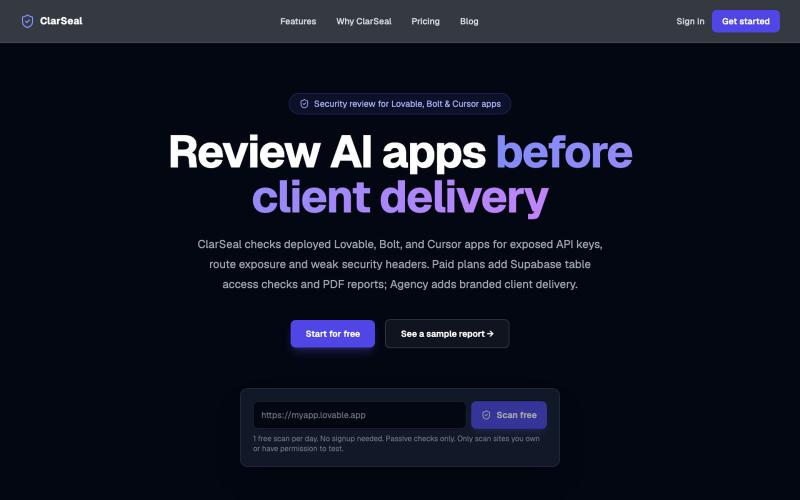
Run point-in-time checks on Lovable, Bolt, and Cursor apps for exposed API keys, Supabase misconfigurations, and weak security headers, then document the findings in a PDF report.
u/arsm2016 · Reddit
I built a security checker for AI-built apps. Looking for 5 builders preparing to launch. I’m building ClarSeal for people shipping apps made with Lovable, Bolt, or Cursor. It scans a deployed app for exposed secrets, security configuration issues, and other observable risks, then provides findings and fix guidance. Paid plans include PDF reports, agencies can also share a branded client report. It’s a scoped automated check, not a full pentest or a guarantee that an app is secure. I’m
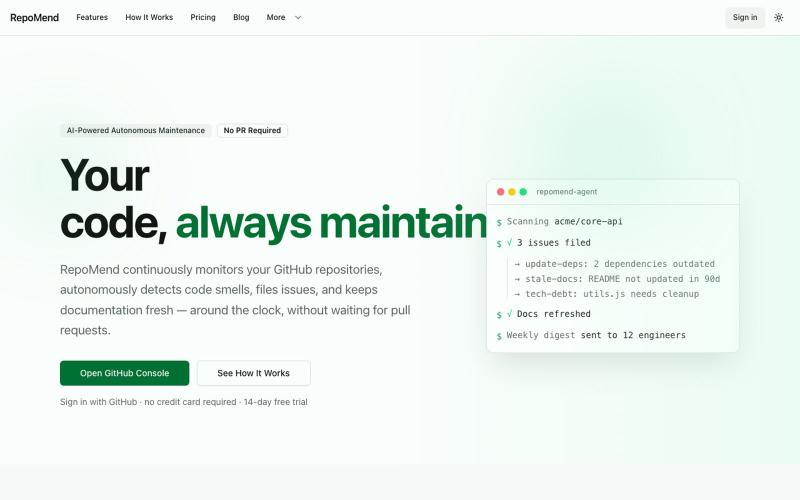
Scans code diffs for security secrets and code quality issues.

@RepoMend02 · X
Vibe-coded your MVP in a weekend? Cute. RepoMend reads every diff and hunts the secrets your AI forgot to redact. The auditor the AI forgot to build.