
Developer Tools3 weeks ago
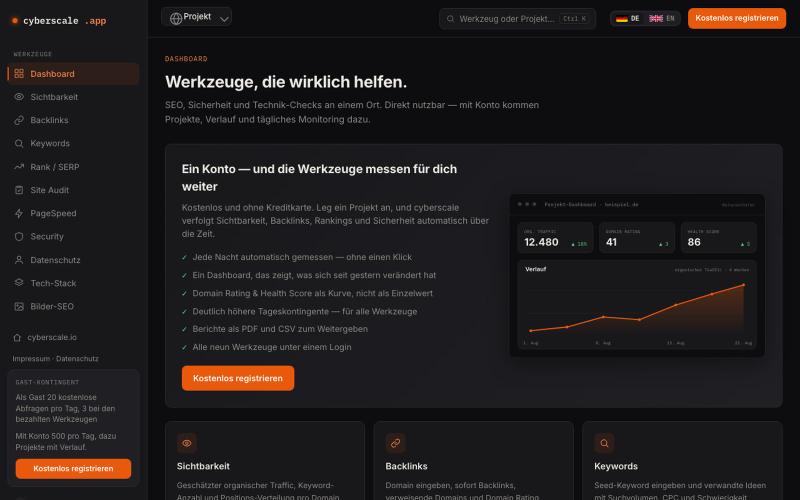
Kostenlose SEO- und Security-Werkzeuge — cyberscale
Sichtbarkeit, Backlinks, Rankings, Site-Audit und Security-Check an einem Ort. Ohne Anmeldung testen, mit Konto Projekte und tägliches Monitoring.

@cyberscaleio · X
The full gallery
Tech stack
60 projects
Sichtbarkeit, Backlinks, Rankings, Site-Audit und Security-Check an einem Ort. Ohne Anmeldung testen, mit Konto Projekte und tägliches Monitoring.
@cyberscaleio · X

See what ChatGPT, Perplexity, Gemini, Claude, and Grok say about your brand, and what happens when people act on it. Cookieless, EU-hosted, live in 60 seconds.
wowinter15 · HN
Voris: privacy-first analytics for the AI-influenced web
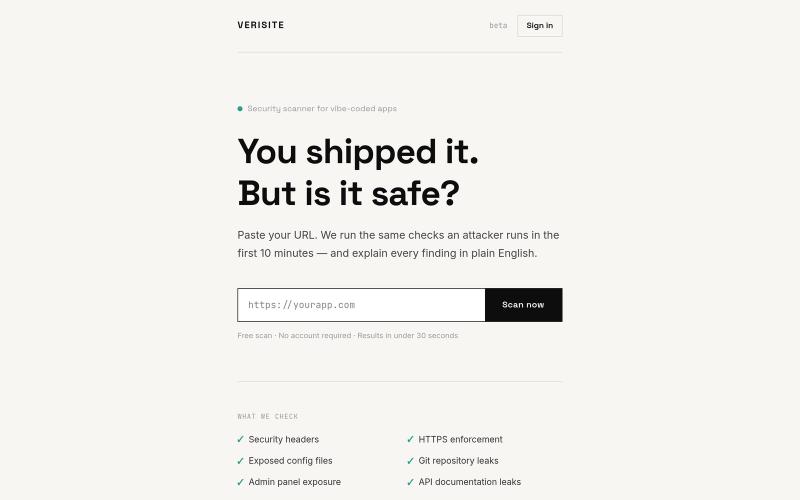
Paste your URL to get security findings for web apps explained in plain English

@luqmandv · X
I built a free security scanner for vibe-coded apps. You shipped with Cursor, Bolt, or Lovable. But did you check if it's actually safe? Paste your URL → get a plain English security report in 30 seconds. No setup! 👉 #buildinpublic #vibecode
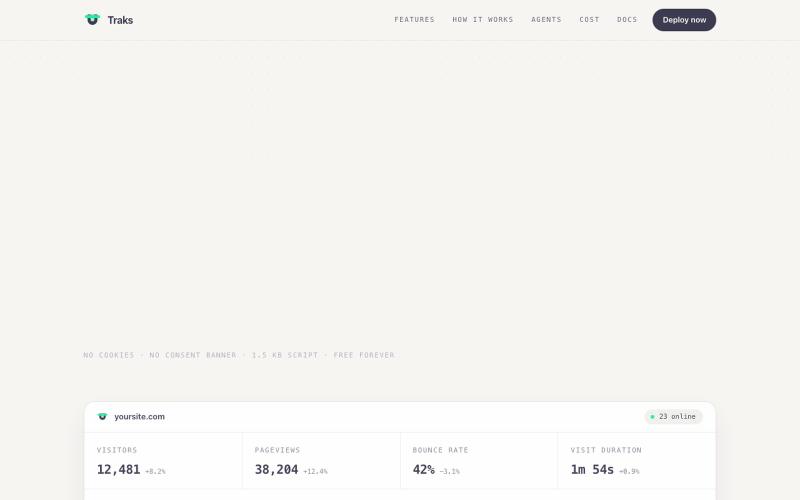
Self-hosted web analytics platform running on Cloudflare without cookies or tracking.

@BinaryScriptar · X
Introducing Traks - free, self-hosted web analytics that runs entirely in your own Cloudflare account. 🚀 It started as a side project. When Cloudflare launched R2 SQL, I wanted to see whether a complete analytics stack could run on their data platform alone: ingest events through Pipelines, land them in R2 as Parquet, and query them straight with SQL. No warehouse, no ETL, no servers to patch, just my personal projects as the first test bed. It worked better than i expected, so I kept adding new features. A few weeks later it's a complete product. What Traks does • Real-time dashboard: visitors, pageviews, bounce rate, visit duration - every metric compared with the period before • Pages, referrers, UTM campaigns, and an AI tab that shows which assistant (ChatGPT, Claude, Perplexity…) sent the visitor • Locations and devices, resolved at the edge without storing IPs • Custom events, goals (incl. path-prefix goals), funnels, saved segments, workspaces & teams • A
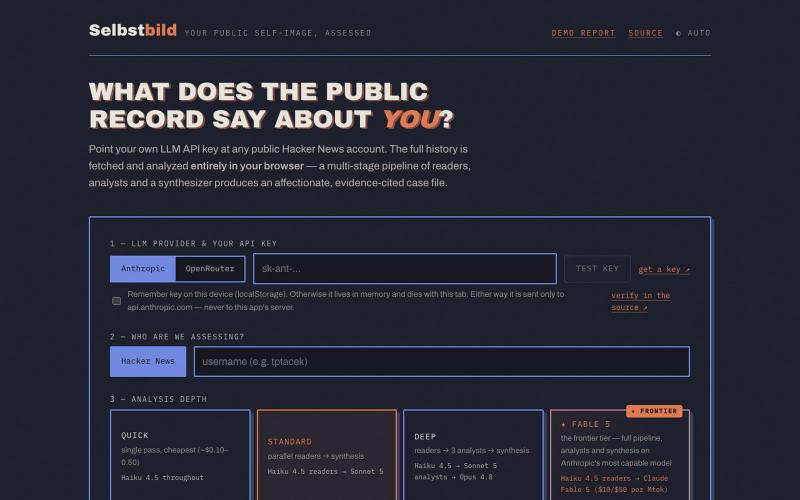
Analyze Hacker News profiles with your own LLM API key, fully client-side.
Topfi · HN
Like everyone on HN, I love nothing more than to (re)read my own comments. Getting my intuition that I am among the smartest, most humble, highest quality commenters on here confirmed by an LLM so capable that the US government had to temporarily export restrict it [0] seemed only natural. Having had my perfection confirmed, I decided to share this joy with you as I had a few percent usage left before a reset. I took a few prompts, then did a review of the output which resulted in Selbstbild, a BYOK (Anthropic / OpenRouter) web app that gives you a summary and assessment of your public comments by one of our machine Gods, including Fable 5 (provided your can afford that luxury at API pricing). In all seriousness, I have, for a long time, used my own comments on social media (including HN) as part of a personal needle-in-haystack test, simply because I do know my somewhat peculiar style and what I tend to write, but also because I can sometimes write in a slightly confusing manner, ma

Scan web apps for security vulnerabilities with 7 scanners and receive AI fix prompts and PDF reports.

@hexorasec · X
Paid Hexora accounts now get PDF security reports. Every finding with evidence, CVSS scores, remediation steps, and AI fix prompts, in a report you can hand to a client or keep for compliance. Live for Starter, Pro, and Max. #buildinpublic #vibecoding
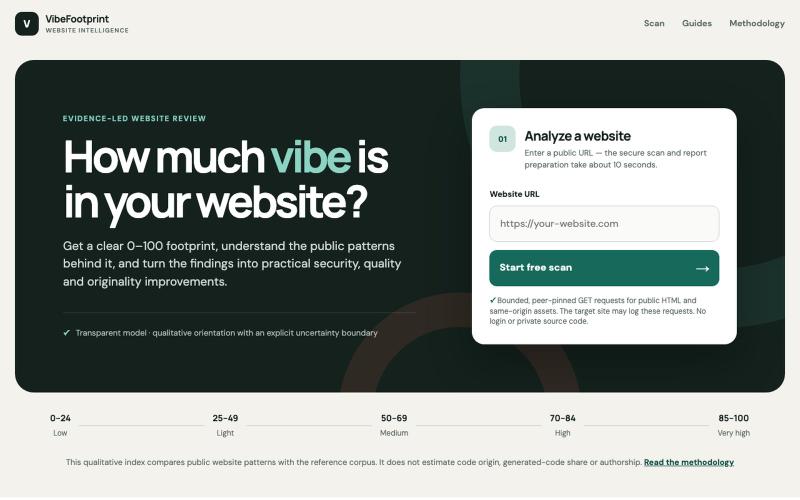
Analyze websites for vibe-coding patterns and security headers without signing in.
u/RockettBits · Reddit
I built a tool that tells you why a website “looks vibe coded” and how to improve it. Some of us use vibe coding because it’s insanely fast, and honestly, a lot of the results are pretty good. But there’s also this weird thing where you open a website and can almost instantly tell it was vibe coded. Same cards, same rounded corners, same gradients, same spacing, same component-library feel. People usually just call it “AI slop,” but I wanted to understand what actually creates that feeling.
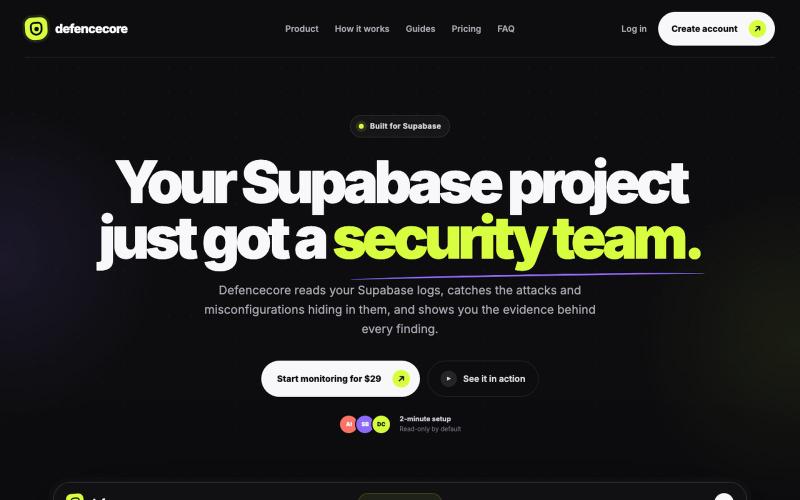
Monitor your Supabase logs for security issues like credential stuffing and exposed keys.

@DefencecorHQ · X
Your app has been live for months. Your last log check was launch day. Defencecore monitors your Supabase activity and surfaces what needs attention—so you don’t have to live in the logs. #vibecoding #ai #supabase

Monitor SSL certificates and website security with continuous checks for renewal, headers, and DNS.

@di_spivak · X
Free privacy and security tools that run entirely in your browser

@VaultY796 · X
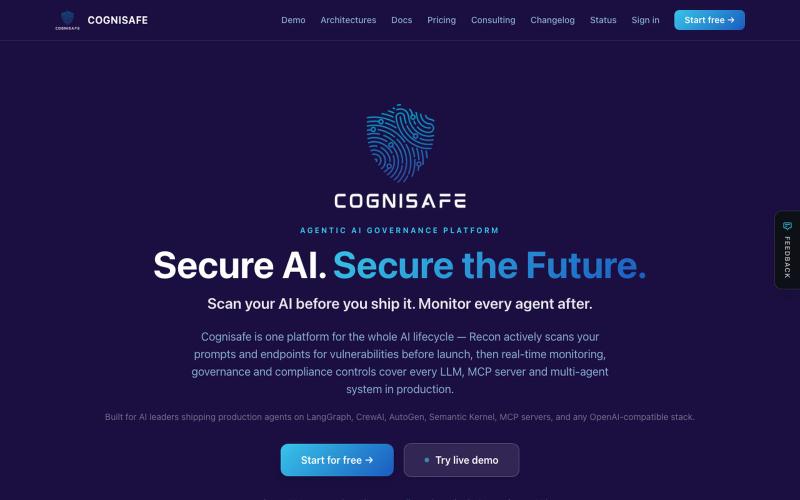
Scan AI prompts and endpoints for vulnerabilities, then monitor LLMs in production for security and compliance.

@CognisafeUK · X
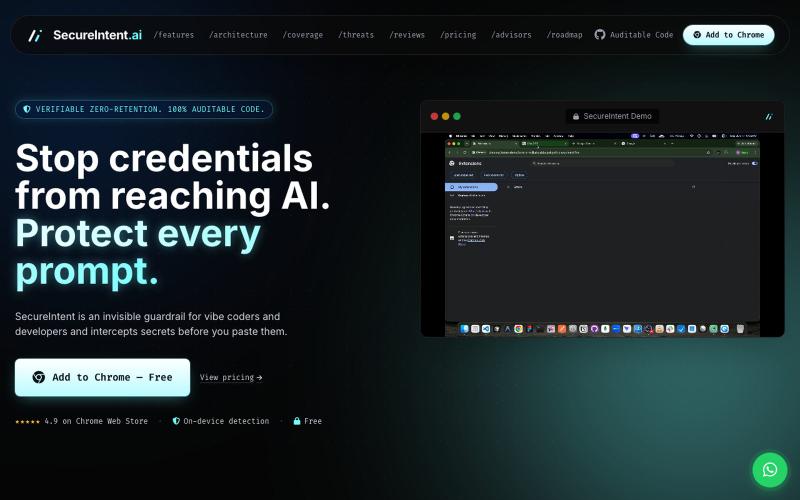
Chrome extension that intercepts secrets before you paste them into AI tools.

@Secureintent_ai · X
SecureIntent is a free Chrome extension that intercepts API keys, tokens, and passwords before you accidentally paste them into AI tools