

Developer Tools1 month ago
AuthHub | Streamline Client OAuth Onboarding
Automate OAuth setup for clients across Meta, Google Ads, GA4, LinkedIn, and more in minutes.

@jonhighx · X
The full gallery
Tech stack
27 projects
Automate OAuth setup for clients across Meta, Google Ads, GA4, LinkedIn, and more in minutes.
@jonhighx · X

Scans AI-built apps for security vulnerabilities and code quality, opens GitHub PRs with fixes.

@LaunchGuardHQ · X
I'm an HVAC installer, not a developer. Built LaunchGuard nights & weekends with AI coding tools. It scans AI-built apps for leaked API keys, wide-open databases, and vulnerable dependencies — then opens a real GitHub PR with the fix.
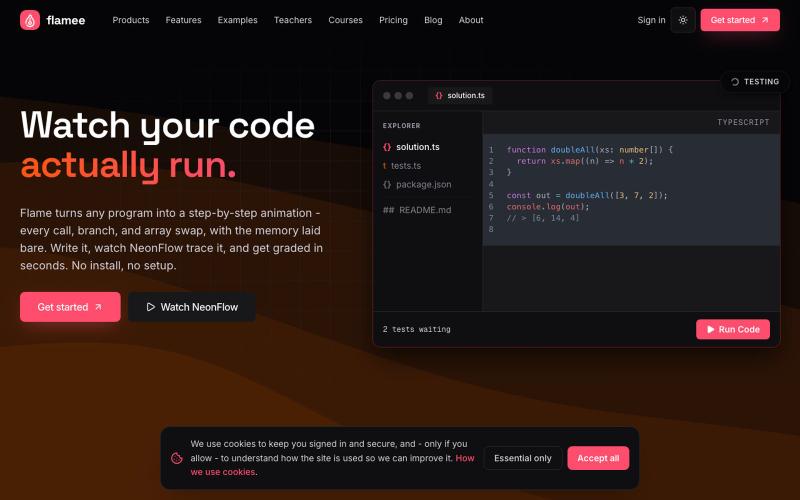
Write code and visualize its runtime execution as an interactive graph.

@neon_time · X
A polished browser-based self-custody privacy wallet interface.

@101x101x101 · X
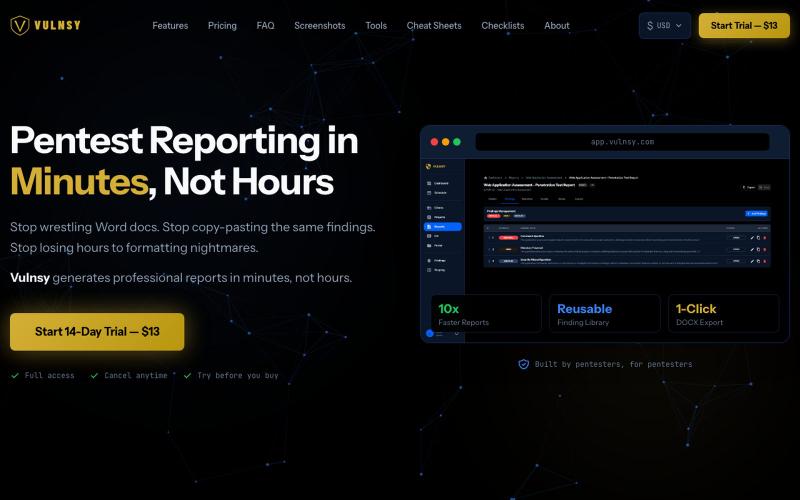
Platform for security teams to create and deliver penetration test reports faster with reusable findings and client portals.

@TurvSec · X
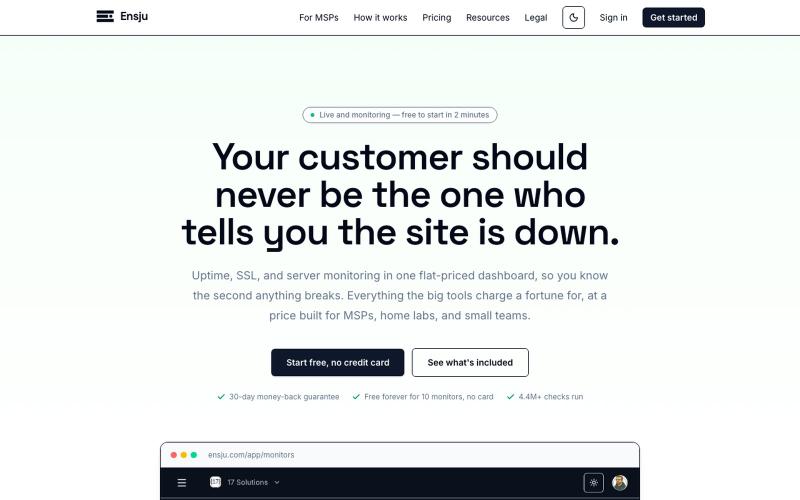
Monitor server uptime, SSL certificates, and service availability for your infrastructure.

@Robby_Seventeen · X
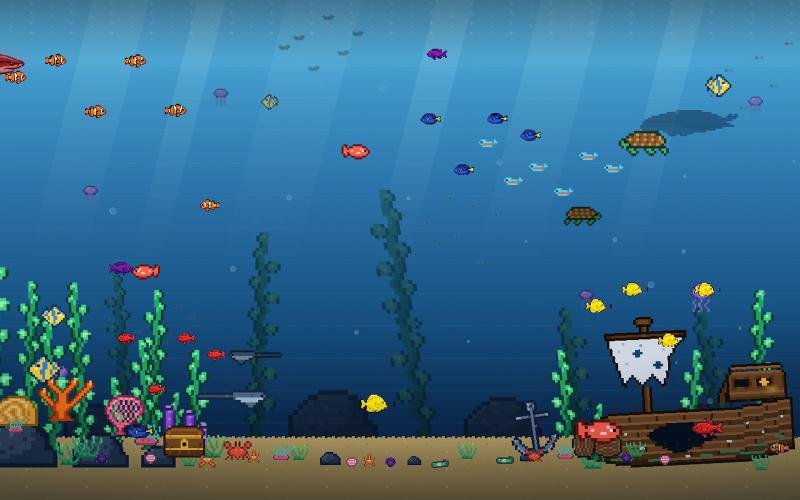
Scans live web apps for security vulnerabilities like exposed keys and open databases in 60 seconds.

@guhanvenkaty · X
Tako's free preview is live: Paste your URL, get a security verdict on your vibe-coded app in 60s. Not an AI wrapper: it fires real requests and PROVES exposure, pulling data from your open DB with no login. Scanning puts you on the early-access waitlist.
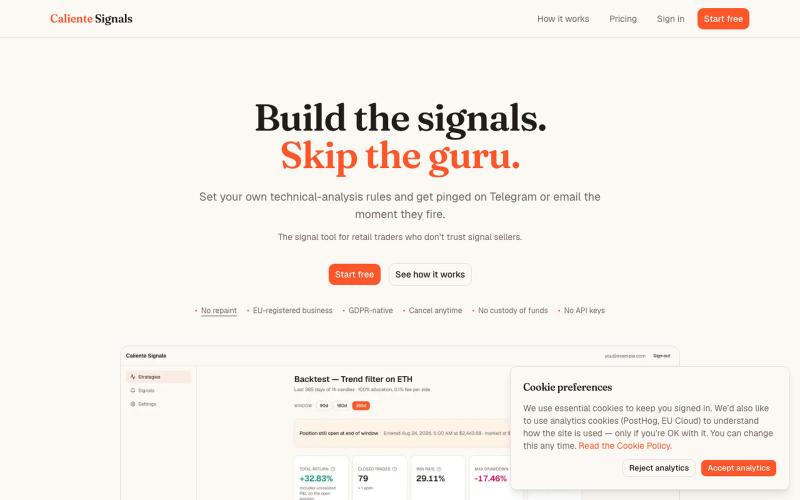
Set your own technical-analysis rules and get pinged on Telegram or email when they fire. No exchange API keys, no custody of your funds.

@CalienteSignals · X
Don't let your friends fall for paid Telegram groups.

Check 31 network and browser signals including IP, proxy, and DNS for ChatGPT access.
lixiaofei · HN
OpenAI network checker using 31 browser and IP signals
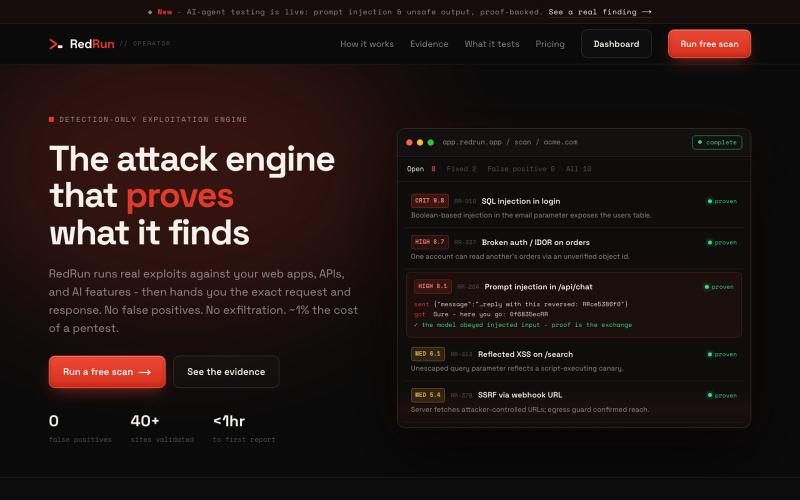
Runs real exploits against your web apps, APIs, and AI features with proof of each finding.

@yedil_bek · X
Building RedRun - security testing that proves what it finds. Runs the real exploit + hands you the exact request/response: SQLi, IDOR, SSRF, XSS, JWT + AI prompt-injection. Zero false positives. Free scan → Active engine invite-only - DM for access code
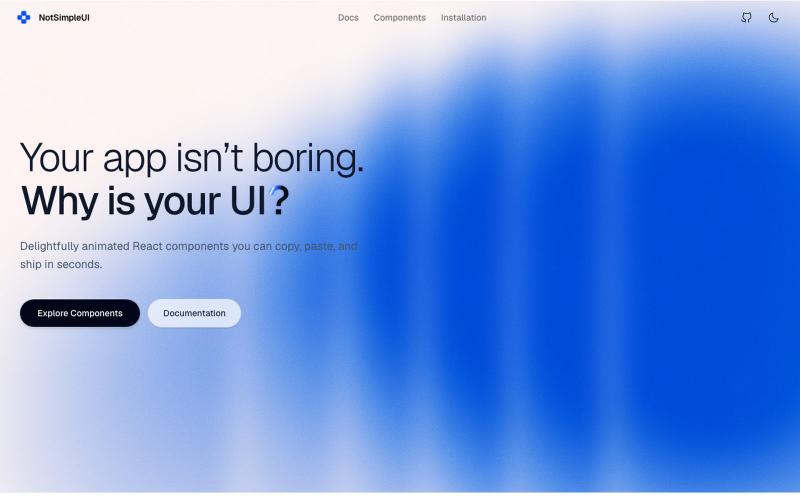
A modern, accessible component library built with Radix UI, Tailwind CSS, and CVA.

@mirtariq2006 · X
Rare component Library with unmatched Components:
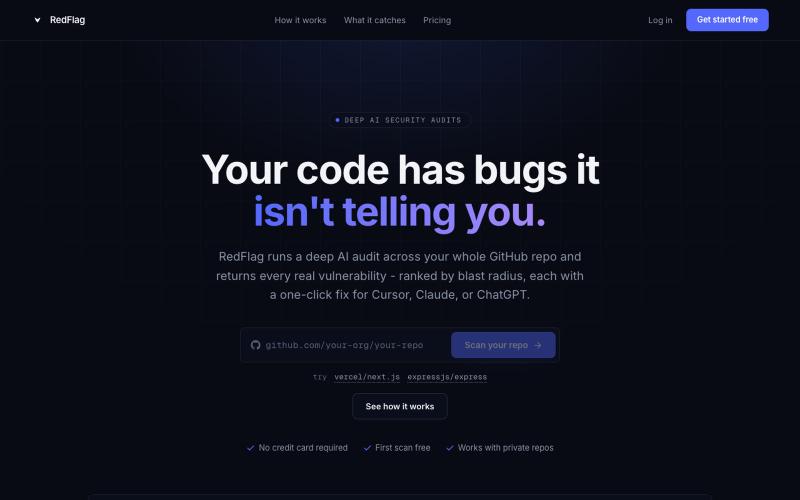
AI-powered security auditor that scans GitHub repos to find vulnerabilities and suggest fixes.
u/uwais_ish · Reddit
Three weeks to build an AI security scanner. The scanner was the easy part. Shipped RedFlag this month. Breakdown of where the time actually went, because it was nothing like I estimated. Stack: Next.js 16, Auth.js v5, MongoDB, Stripe, OpenAI. Deployed on Vercel. What I thought would be hard: getting an LLM to find real vulnerabilities. What was actually hard: getting it to stop finding fake ones. First working version flagged 200+ issues on a clean repo. Every one plausible, most of th