
Productivity2 months ago
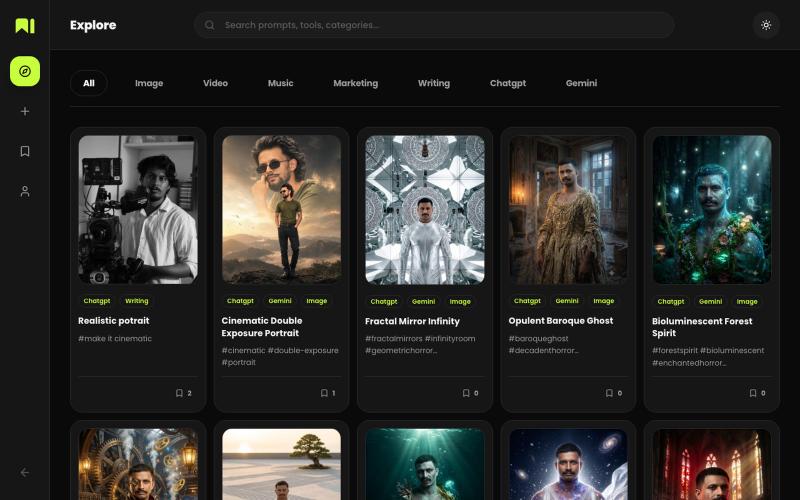
Explore AI Prompts · Saveaiprompt
Explore community-reviewed AI prompts organized by tool, category, and workflow.

@Utsabpanday · X
The full gallery
Tech stack
18 projects
Explore community-reviewed AI prompts organized by tool, category, and workflow.
@Utsabpanday · X

Turn your Claude and ChatGPT conversations into prompt reviews and reusable habits.

@OCoolhead · X
vibe coded this app from my phone 😂 !! Prompt Habbit convert your chatgpt/claude chat sessions into prompt reviews, yes similar to github PR review. Create an agentic loop from your chat sessions. -> for your next prompt review Crazyy that you can give prompt in vpn and see the update coming on the live website. Thanks @zeropsio @WeMakeDevs
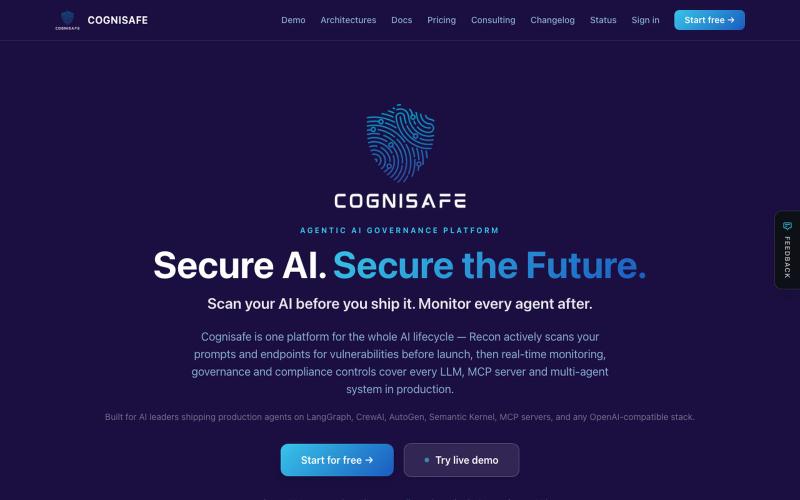
Scan AI prompts and endpoints for vulnerabilities, then monitor LLMs in production for security and compliance.

@CognisafeUK · X
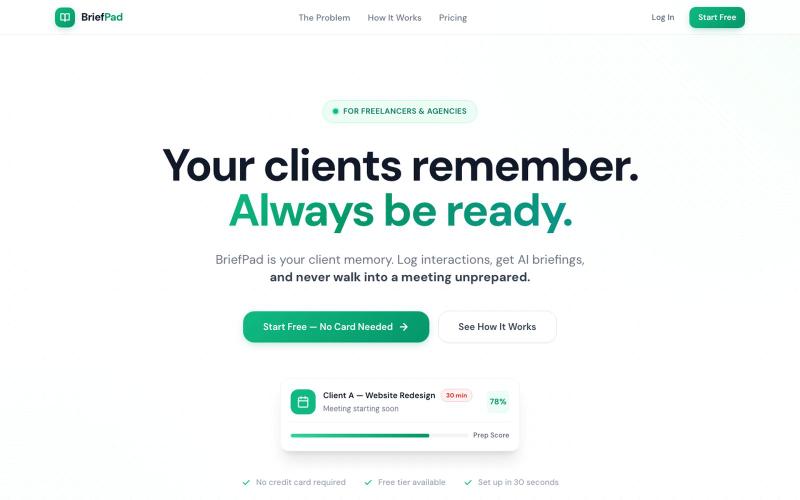
Store client notes and get AI-generated briefings before meetings.

@yohannes_mulaw · X
🚀 vibe coded and shipped an tool called BriefPad. An AI-powered meeting prep tool that helps you walk into every client meeting prepared. Built it from scratch and it’s live 👇 Feedback welcome!

Scan code and applications for vulnerabilities using AI-augmented security analysis.
u/swifi_ai · Reddit
After 10 years of keeping this idea alive, I finally launched my AI security platform to beta After more than 10 years of keeping this idea alive in one form or another, I finally pushed Swifi live to beta: https://swifi.ai Swifi is an AI-augmented application security platform. The goal: combine traditional security scanning with AI so teams can understand risk across code, vulnerabilities, and production context without stitching together a dozen disconnected tools. Why now? AI change
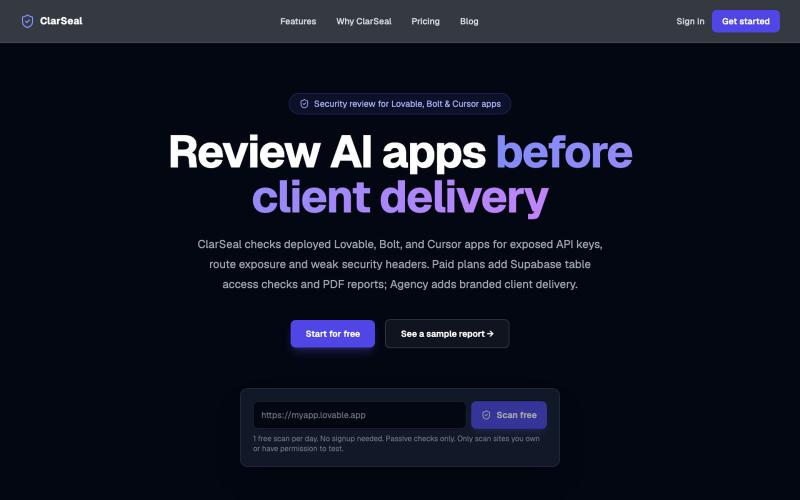
Run point-in-time checks on Lovable, Bolt, and Cursor apps for exposed API keys, Supabase misconfigurations, and weak security headers, then document the findings in a PDF report.
u/arsm2016 · Reddit
I built a security checker for AI-built apps. Looking for 5 builders preparing to launch. I’m building ClarSeal for people shipping apps made with Lovable, Bolt, or Cursor. It scans a deployed app for exposed secrets, security configuration issues, and other observable risks, then provides findings and fix guidance. Paid plans include PDF reports, agencies can also share a branded client report. It’s a scoped automated check, not a full pentest or a guarantee that an app is secure. I’m