
完整作品展
技术栈
60 projects
通过审问员工和分析日志来找出内部威胁的网络安全侦探RPG游戏。

@geeky_gamer25 · X
Check out what I just built with Lovable!
扫描AI提示词和端点的漏洞,实时监控生产LLM的安全性和合规。

@CognisafeUK · X
Chrome扩展,在粘贴到AI工具前拦截您的API密钥和密码。

@Secureintent_ai · X
SecureIntent is a free Chrome extension that intercepts API keys, tokens, and passwords before you accidentally paste them into AI tools
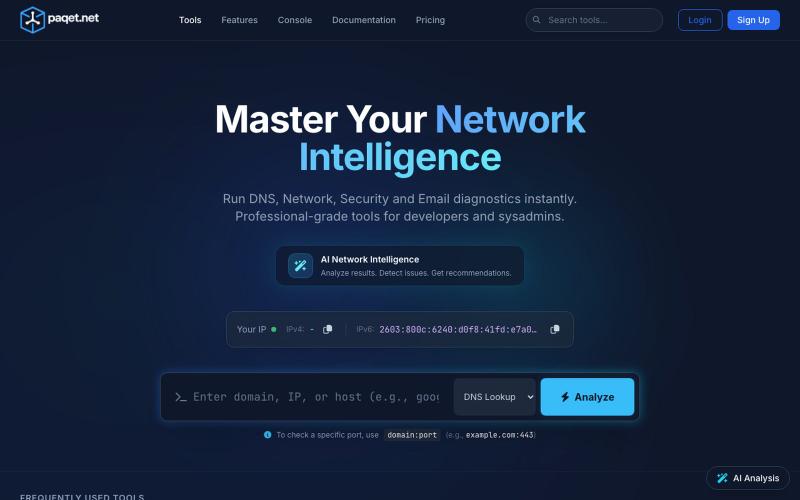
一站式AI网络诊断工具,支持DNS、SSL和数据包分析。

@paqetnet · X
Building Paqet — DNS, SSL, network & email diagnostics in one place, built to actually be usable. Describe your issue, AI runs the checks and tells you what's wrong + what to do next. Solo-built, free to try, API included 🛠️
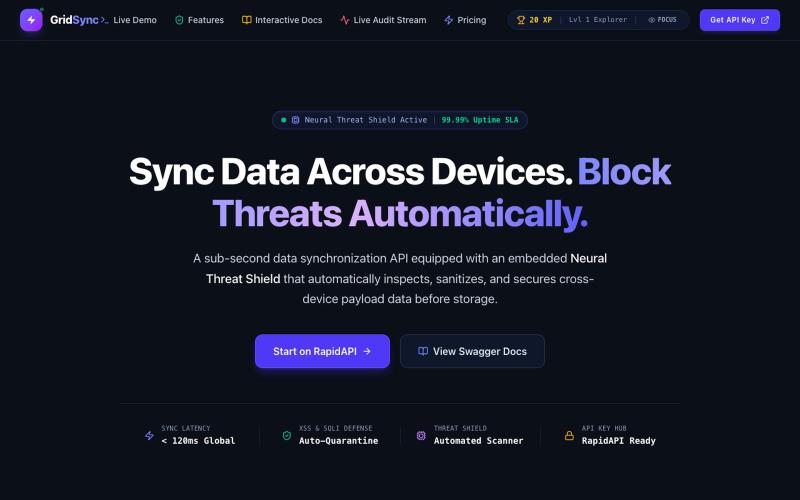
通过 GridSync API 实时同步跨设备数据,具有自动威胁检测和清理功能。

@mygridsyncdev · X
Just launched GridSync ⚡️ Sub-150ms zero-trust payload inspection & real-time sync for modern APIs. Try the free tier on RapidAPI or check out the docs: #buildinpublic #API #FastAPI

在加密工作区中与 Claude Code 和 Cursor 等 AI 代理共享文件和日志。

@Raullen · X
6 months ago, @qevan and I hit a stupid wall: just trying to share a local file or some logs with an AI agent was incredibly frustrating. So, we built the first version of —a dead-simple, secure way to pass context to AI. The community feedback was amazing. We got ~200 stars on GitHub, and it quickly became a daily driver for a lot of developers. But recently, we realized the game has changed. Our workflows evolved. It’s no longer just humans sending files to agents. Agents need to write back to humans. Agents need to hand off context to other agents. The whole team—human and AI—needs to collaborate. So, we gave vnsh a massive upgrade. Today, it’s no longer just a secure clipboard. It’s now a living workspace. 🚀 You drop your context in once and get a dynamic link. Claude Code, Cursor, Cline, and your human teammates all open the exact same document. When one agent updates it, your whole stack sees it instantly. Complete context handoff, without ever copy-pastin

检查你的简历是否通过ATS系统筛选,获得优化建议。

@Patryk597153122 · X
Stwórz profesjonalne CV i sprawdź, czy przejdzie przez systemy ATS 👇 Zwiększ swoje szanse na znalezienie pracy

为网络设备自动备份配置并用E2EE端到端加密保护。
Willdom1986 · V2EX
多年前考过 CCNP 网络工程师,以前有一个很头疼的地方就是网络设备配置丢失引发的各种故障。后来越发觉得,网络设备的配置实际上是一个非常关键的数字资产。 为此,我利用周末时间开发了 XConf ( https://xconf.ai) 来解决这个问题。 产品主要就是想解决两个问题:**自动化的灾备高可用**,以及**端到端的安全**。 * **自动备份与灾备**:支持将配置定时备份到云端。如果网络断连了,探针会自动在本地离线队列里暂存配置,等连接恢复后自动重传。 * **端到端加密**:本地的 Go 探针是完全开源的,会自动在内存中对密码进行流式脱敏,并在上传前通过 AES-256-GCM 在本地加密。SaaS 后台拿到的只有密文,解密和版本比对( Diff )都完全在你的浏览器本地沙盒里通过 WebCrypto API 进行。 * **打磨版的配置对比 Diff**:我花了一些功夫打磨了浏览器端的配置版本对比功能,力求让日常比对的交互体验足够丝滑。 * **AI 安全基线审查**:系统集成了 AI 辅助的安全基线审查,可以一键检查和分析配置中的潜在风险。 因为目前完全是我利用业余时间(主要在周末)维护,所以确实没精力提供工作日的在线即时客服。大家使用过程中遇到任何 Bug ,欢迎随时去 GitHub 提 Issue ,我会在周末集中修复和跟进。 目前公测已开放,不需要邀请码即可注册,欢迎大家体验吐槽。 探针 agent 开源地址: https://github.com/willdom-lee/xconf-agent 官方网站: https://xconf.ai

用AI搜索自由职业工作,生成提案,评估客户风险。

@ToobaNisariwk3 · X
FreelanceAI – A modern AI SaaS UI/UX package with responsive screens, source code, documentation, demo video, screenshots, and a live demo. Demo:
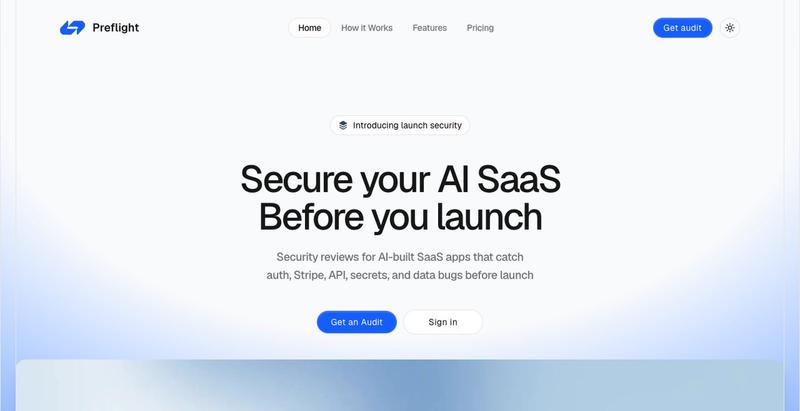
为GitHub仓库运行安全审计,检测密钥泄露、认证问题和部署漏洞。

@emanueldev4 · X
Building Preflight a simple way to catch issues before your website goes live.
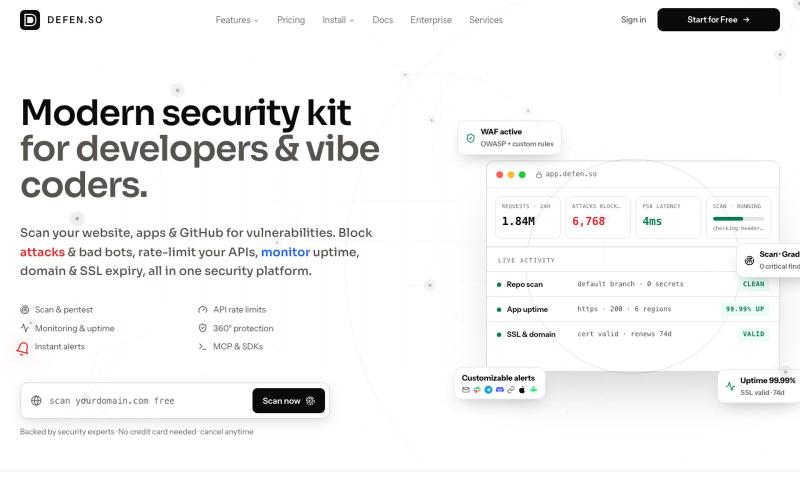
网站安全扫描工具,提供WAF保护、运行时间监控和SSL证书管理。

@YounesLamnabhi · X
a mist to have security kit, pentest and monitoring, can be installed in seconds.
