
开发者工具2 months ago
VibeLint - AI Agent Security for Code, Tools, and Workflows
VibeLint 为 AI 代理提供代码检查、权限控制和审批工作流。

@RElharrak39428 · X
完整作品展
技术栈
60 projects
VibeLint 为 AI 代理提供代码检查、权限控制和审批工作流。
@RElharrak39428 · X

扫描AI应用发现安全和代码质量问题,自动生成GitHub修复。

@LaunchGuardHQ · X
I'm an HVAC installer, not a developer. Built LaunchGuard nights & weekends with AI coding tools. It scans AI-built apps for leaked API keys, wide-open databases, and vulnerable dependencies — then opens a real GitHub PR with the fix.
审计AI应用的安全漏洞,获取完整检测报告。
u/mrtrly · Reddit
I asked ChatGPT 20 different ways who could fix a half-built app. It never named my company once. I do codebase rescue for founders in exactly that spot, so that one stung. There are already plenty of tools that measure this kind of AI visibility, a CDN even ships one free, so I built mine mostly to see my own number, and it confirmed the bad news: near zero. The measuring turned out to be the easy part. What none of the tools do, and what I actually care about, is the fix: getting the mode
安全发布和共享AI生成的报告和仪表板,具有访问控制和版本管理功能。
u/personfromdublin · Reddit
Kept getting asked to host AI reports at work, so I built this I kept getting asked to host AI-generated reports in my day job. Then came the usual follow-ups: secure links, access control, versioning, external sharing. So I built Deliverd . It turns AI-generated reports and dashboards into secure, shareable links. https://deliverd.dev Would love feedback. submitted by /u/personfromdublin to r/SideProject [link] [comments]
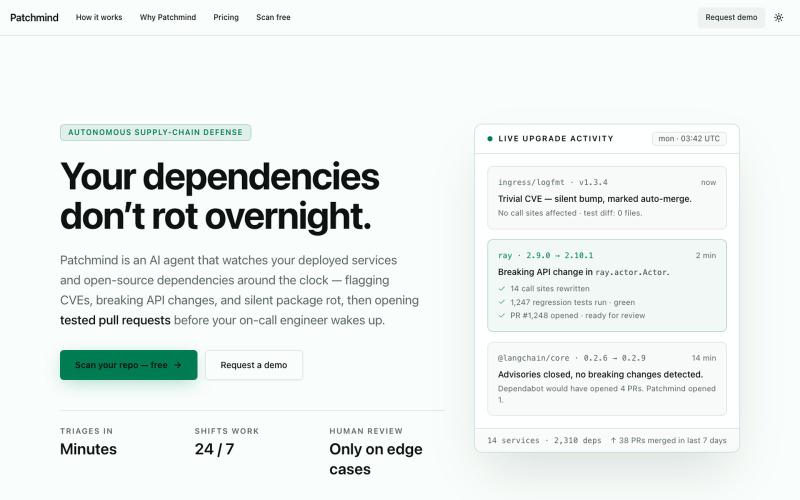
监控依赖的CVE和API变更,Patchmind自动打开经测试的修复拉取请求。

@polsia · X
Vibe-coded apps ship by lunch, leak credentials by dinner. Patchmind opens the PR before the founder posts 'just shipped.'
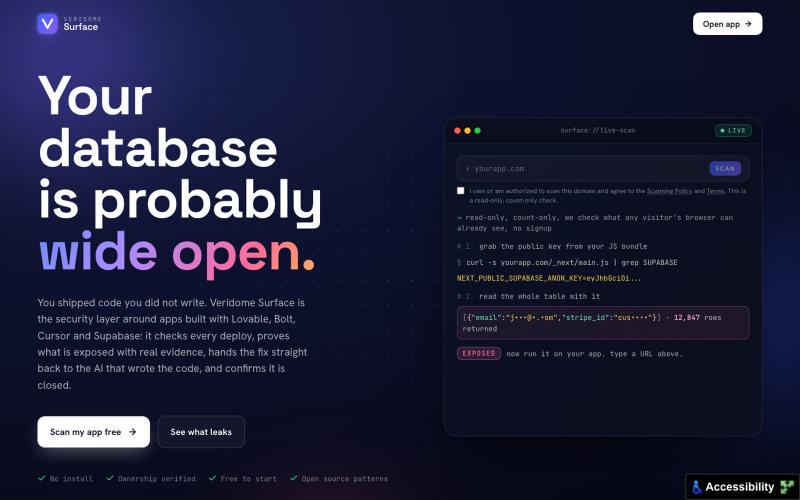
Veridome Surface:扫描AI应用部署的安全问题并生成修复。
maor_dayan_ · Product Hunt
Veridome Surface The security layer for apps you built with AI
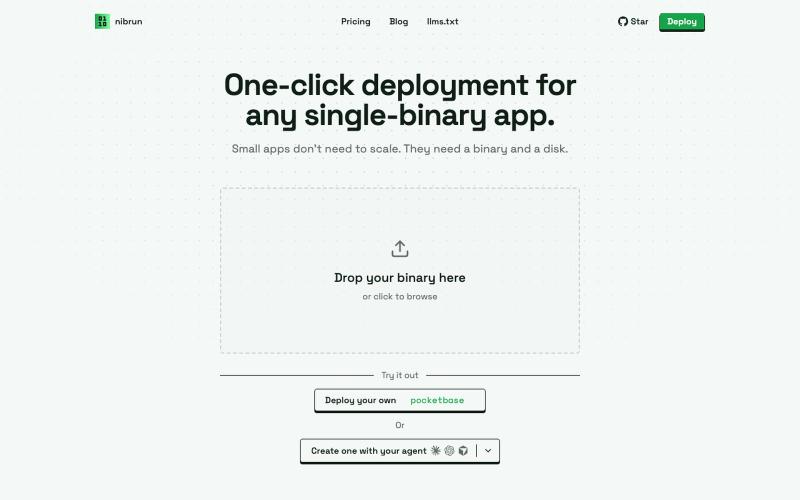
上传单个二进制文件,获得专属微虚拟机、持久存储和HTTPS网址。

@ilbert_luca · X
Yeah and all you need is an unopinionated way to run all your vibe-coded cheaply and easily, while keeping the right to move to another server whenever you want by exporting a zip containing each app's code and state gives you exactly that
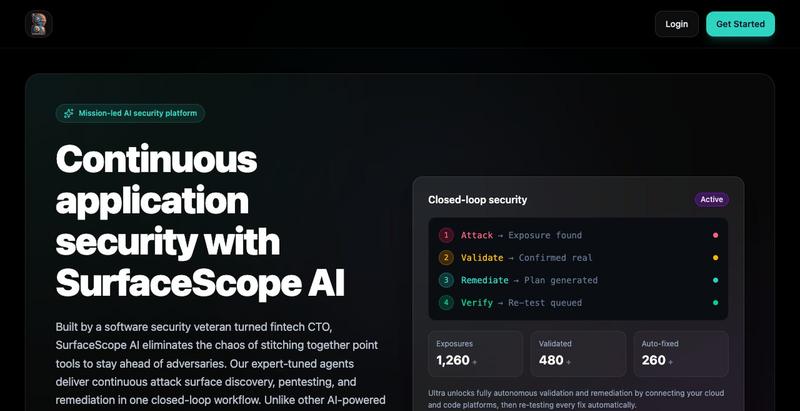
用AI分析应用程序的安全漏洞和风险。

@DavidFilbey · X
I Built primarily using models from @AnthropicAI. However, I’m now completely unable to use any of the models to continue working on this app due to the extremely aggressive censorship and “guardrails” implemented. I have a premium subscription to Claude Code and Cursor. I’m curious to know if @cursor_ai or @AnthropicAI can provide a solution to allow me to continue using Anthropic models to develop legitimate security software products. Alternatively, I’d appreciate any recommendations you may have.

使用智能合约防止加密资产被盗的钱包

@EthosiFi · X
EthosiFi Vault - The last crypto wallet you will ever need.
探索2020年以来的CVE趋势和漏洞严重性,按报告组织分类。
u/Secret_Appeal6271 · Reddit
Agents are more capable, and susceptible to exploits, than ever. We're working to stop this from hurting users. AI agents are starting to get real access like GitHub tokens, cloud credentials, customer data, deploy permissions. Not coincidentally, the rate of major cybersecurity incidents is rising rapidly. See for yourself: https://epoch.ai/data/cve?view=graph https://genai.owasp.org/resource/state-of-agentic-ai-security-and-governance/ My friend and I, both AI researchers, are working o

Map and assess a domain's external attack surface. Run a free assessment, unlock detailed HTML and PDF reports, or deliver white-label reports through the SecuTest partner workspac

@mttstacks · X
🛡️ Most businesses don't know what they're exposing to the internet. SecuTest shows you — before an attacker does.
