
开发者工具3 weeks ago
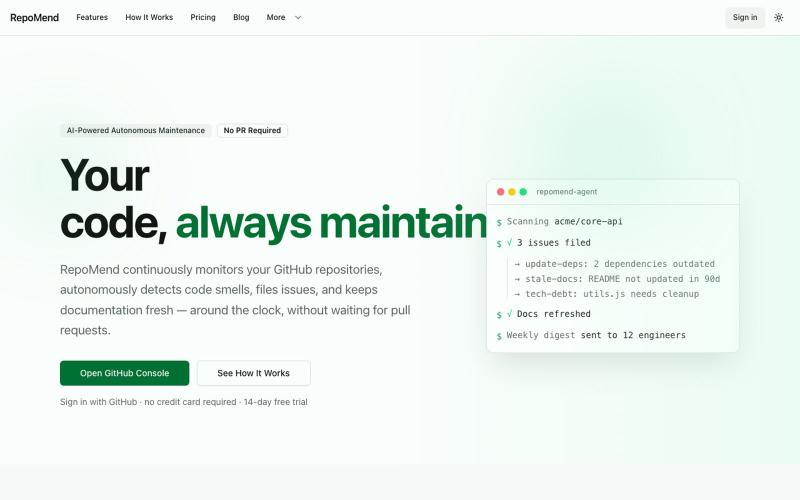
RepoMend
自动扫描代码变更,发现安全问题和代码质量缺陷。

@RepoMend02 · X
Vibe-coded your MVP in a weekend? Cute. RepoMend reads every diff and hunts the secrets your AI forgot to redact. The auditor the AI forgot to build.
完整作品展
技术栈
60 projects
自动扫描代码变更,发现安全问题和代码质量缺陷。
@RepoMend02 · X
Vibe-coded your MVP in a weekend? Cute. RepoMend reads every diff and hunts the secrets your AI forgot to redact. The auditor the AI forgot to build.

使用AI增强的安全分析扫描代码和应用漏洞。
u/swifi_ai · Reddit
After 10 years of keeping this idea alive, I finally launched my AI security platform to beta After more than 10 years of keeping this idea alive in one form or another, I finally pushed Swifi live to beta: https://swifi.ai Swifi is an AI-augmented application security platform. The goal: combine traditional security scanning with AI so teams can understand risk across code, vulnerabilities, and production context without stitching together a dozen disconnected tools. Why now? AI change
使用硬件认证和OTP保护GitHub拉取请求。
jallmann · HN
> want without a PR process that requires hardware authentication or proof of presence Just curious, what do you use for this? I built OTP Guard [1] a few years ago for exactly this problem, although I haven't seen any alternatives in the space. Does GitHub have something built-in now? The original framing was more "local malware compromising your GitHub account" ... it never occurred to me that the malware could be a LLM. I really should update the page. [1] https://otpguard.com

与AI渗透测试代理聊天扫描Web应用和API的安全漏洞。

@SableOffensive · X
Building Sable. An AaaS where specialized AI security agents perform penetration testing for web apps and APIs, helping teams find vulnerabilities before they reach production.
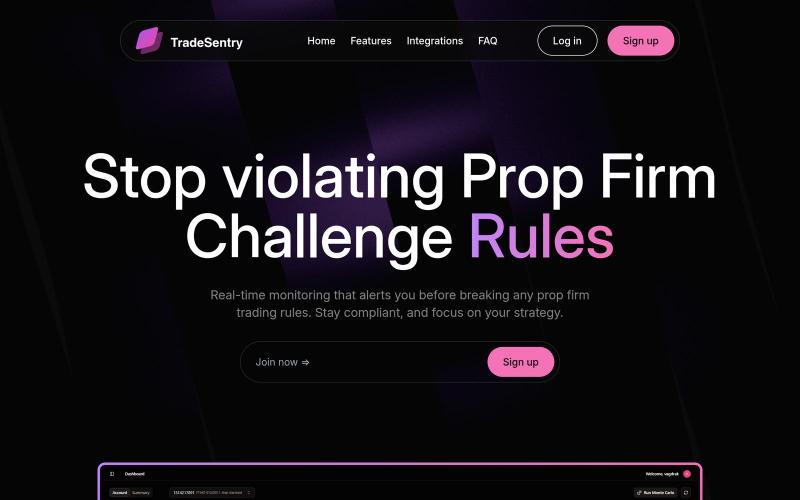
Real-time compliance monitoring tool for prop traders. Get instant alerts for rule violations, risk limit breaches, and time restrictions. Pass your prop firm challenge with confid

@vaggelisdrak · X
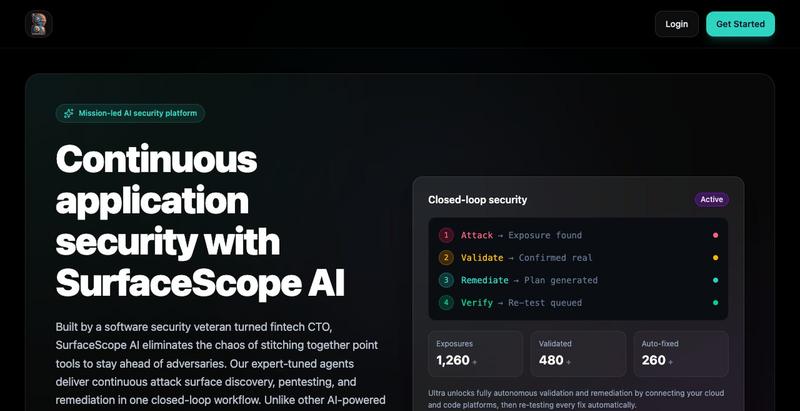
用AI分析应用程序的安全漏洞和风险。

@DavidFilbey · X
I Built primarily using models from @AnthropicAI. However, I’m now completely unable to use any of the models to continue working on this app due to the extremely aggressive censorship and “guardrails” implemented. I have a premium subscription to Claude Code and Cursor. I’m curious to know if @cursor_ai or @AnthropicAI can provide a solution to allow me to continue using Anthropic models to develop legitimate security software products. Alternatively, I’d appreciate any recommendations you may have.

统一代码协助、交易工具和团队协作功能的AI驱动平台。

@ThrillStack · X
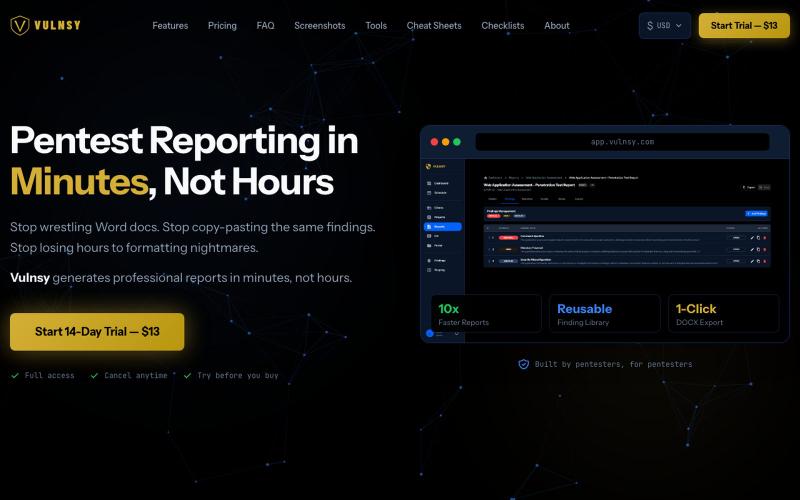
Vulnsy是为安全团队提供的渗透测试报告平台,可10倍快速交付客户报告。

@TurvSec · X
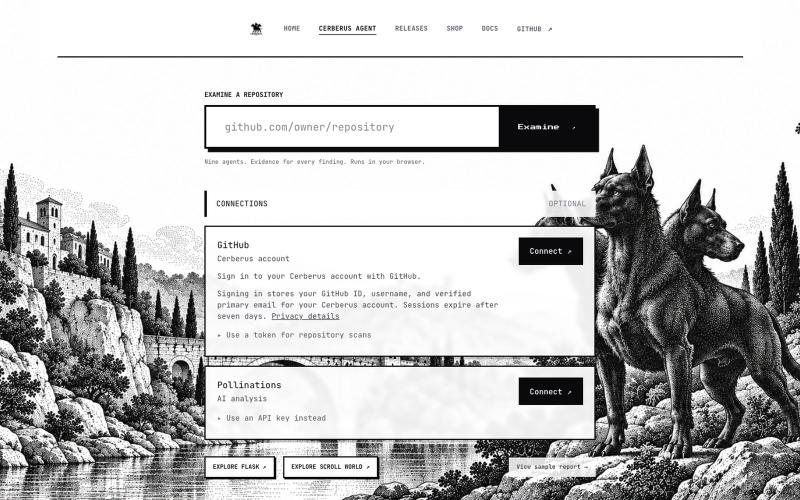
用九个 AI 安全代理分析 GitHub 仓库,查找安全问题并导出报告。
murderszn · HN
GPT 6 Astra gave me a reason to put the finishing touches on an old project, and I'm very content with where it landed. Back in June, I built Cerberus Agent as an AI "watchdog" for vibe-coded apps. The goal was to catch security issues before they turn into hacked apps, leaked credentials, or stolen data. Now its in production! Easier than I though it would be. It uses Pollinations as the AI backend to review GitHub repos, explain findings, and propose fixes. You can discuss the findings, inspec
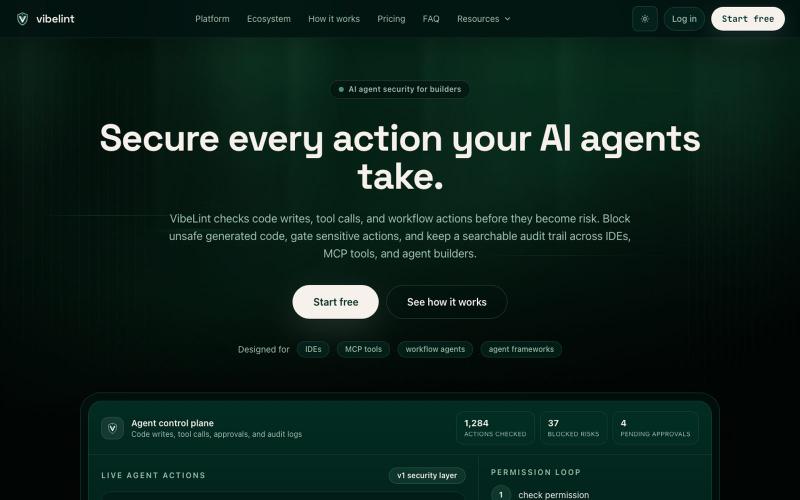
VibeLint 为 AI 代理提供代码检查、权限控制和审批工作流。

@RElharrak39428 · X
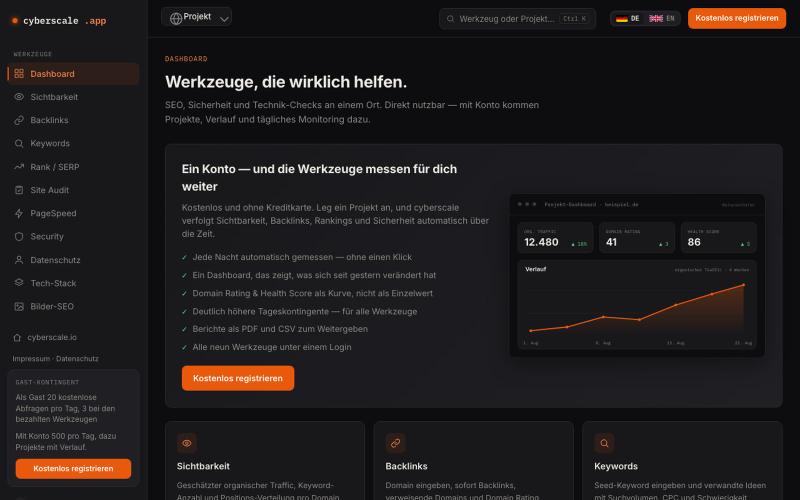
Sichtbarkeit, Backlinks, Rankings, Site-Audit und Security-Check an einem Ort. Ohne Anmeldung testen, mit Konto Projekte und tägliches Monitoring.

@cyberscaleio · X
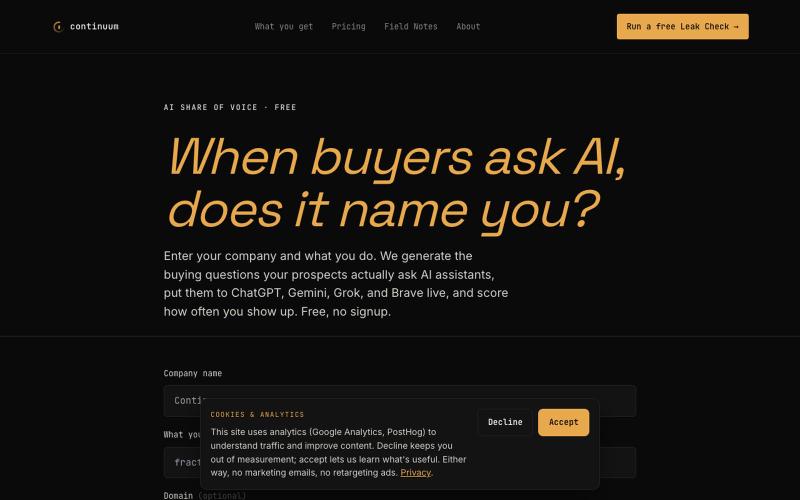
审计AI应用的安全漏洞,获取完整检测报告。
u/mrtrly · Reddit
I asked ChatGPT 20 different ways who could fix a half-built app. It never named my company once. I do codebase rescue for founders in exactly that spot, so that one stung. There are already plenty of tools that measure this kind of AI visibility, a CDN even ships one free, so I built mine mostly to see my own number, and it confirmed the bad news: near zero. The measuring turned out to be the easy part. What none of the tools do, and what I actually care about, is the fix: getting the mode